BIS

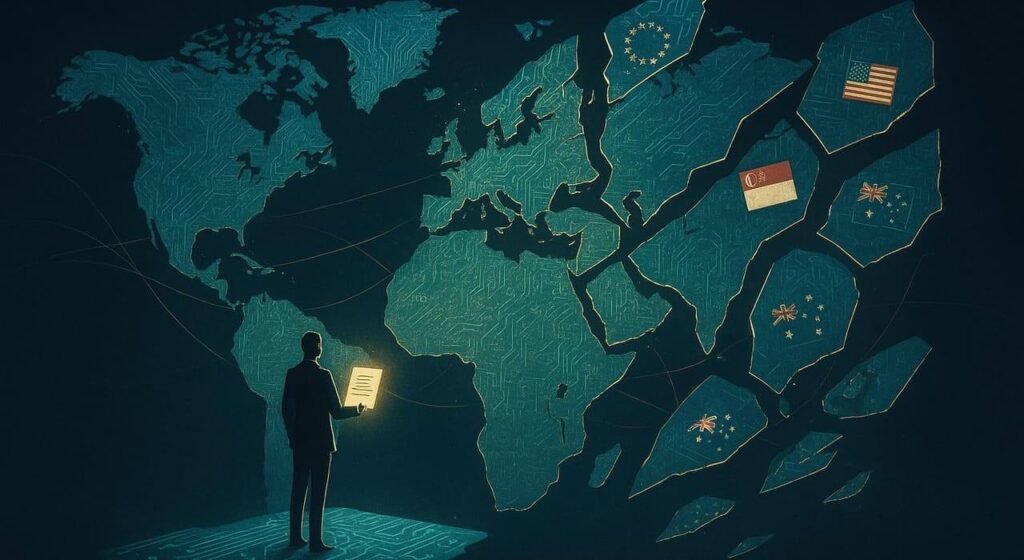
One World, Many Rulebooks: Surviving Fragmented Cyber Compliance

Once upon a time, global cybersecurity compliance had the clean geometry of a well-drawn circuit.ISO 27001 was the north star, NIST SP 800-53 its American dialect, and SOC 2 the accountant’s accent that made it all sound legitimate.If your policies aligned and your audit passed, you could tell the board: we’re secure. That illusion has […]

One World, Many Rulebooks: Surviving Fragmented Cyber Compliance Read More »
Why Financial AI Governance Needs a Global Risk Framework

The Fragmented Future of Financial AI From high-frequency trading to credit scoring and fraud detection, artificial intelligence (AI) is transforming the financial sector. Yet this transformation is unfolding faster than the regulatory frameworks meant to manage its risks. In regions like the EU, U.S., and China, policymakers have launched vastly different approaches to AI governance

Why Financial AI Governance Needs a Global Risk Framework Read More »